
Cyber Security Risk, Governance,
& Management
Protecting the systems care depends on.
A security incident in most industries is a business disruption. In healthcare, it reaches the patient.
When an electronic health record goes offline, clinicians revert to paper and procedures are delayed. When a claims platform stops processing, member service and provider payment stop with it.
Elevance Solutions delivers comprehensive managed security and risk management for hospitals and health plans. Our programs are built around a principle that separates healthcare from every other sector: security must protect the organization without ever standing between a clinician and the patient in front of them, or between a member and the coverage they are entitled to.
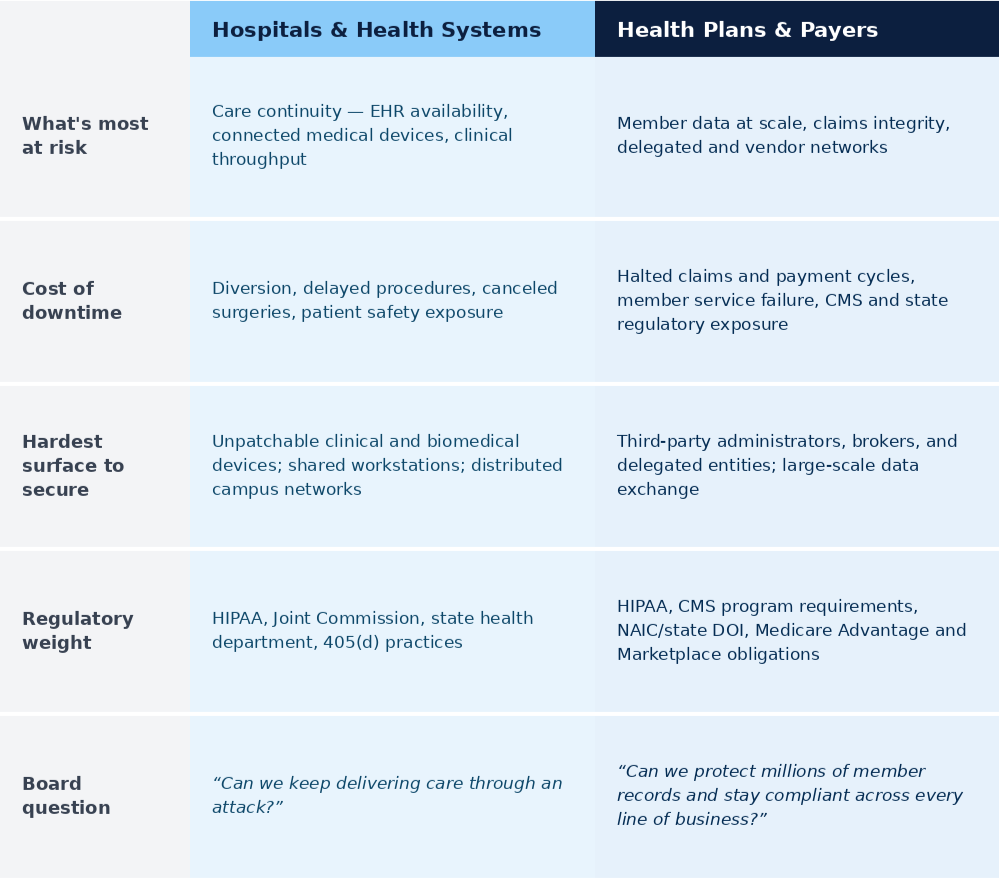
The threats are shared. The consequences are not. We tailor delivery accordingly.
Two Environments, Two Risk Profiles
How safe is your Healthcare environment?
24/7/365 Security Operations · HIPAA & HITRUST-aligned · NIST CSF mapped · Healthcare threat intelligence.
Request a security posture assessment today.
Capabilities
Security Center Operations (SOC)
Continuous vigilance, informed by operational context.
Our SOC monitors your clinical, administrative, and infrastructure environments around the clock, operating Security Information & Event Management (SIEM) and Security Orchestration, Automation, and Response (SOAR) platforms tuned to healthcare threat behavior — ransomware staging, credential misuse, lateral movement toward core systems, and irregular access to protected health information.
-
Escalation and containment decisions are guided by clinical impact. Isolating a compromised segment during a surgical block is a different decision than isolating it overnight, and our runbooks reflect that. We build and rehearse response procedures with your CMIO, nursing leadership, and emergency management team so downtime protocols, device isolation sequences, and patient safety implications are settled before an incident, not during one.
-
Containment is coordinated around claims cycles, enrollment periods, and member service commitments. We account for open enrollment volume, CMS submission deadlines, and delegated vendor dependencies — and we produce the documentation your compliance and legal teams need for regulator and member notification obligations on the timelines those obligations impose.
Artificial Intelligence
A vital need for governance and ethics.
As teams adopt AI capabilities, a new category of risk accompanies them: protected health information entering unmanaged models, unsanctioned tools operating outside IT visibility, algorithmic bias influencing decisions, and unclear accountability when a model contributes to an adverse outcome.
-
The exposure centers on ambient documentation, clinical decision support, and diagnostic assistance — where model error reaches patient care directly.
-
It centers on utilization management, coverage determination, and risk adjustment — where model bias reaches members as denied or delayed care and draws direct regulatory scrutiny.
We help you establish the governance to address both: acceptable use policy, model inventory and approval workflow, PHI data handling standards, bias and drift monitoring, human-in-the-loop requirements for clinical and coverage determinations, and documentation aligned to emerging regulatory expectations.
Our objective is to make AI adoption safe, not to make it slower.
Cloud Security
Consistent governance across a footprint that grew one workload at a time.
We establish and maintain a unified security posture across AWS, Azure, Google Cloud, and the SaaS platforms already in use across your organization: posture management, workload and container protection, cloud identity and entitlement governance, encryption and key lifecycle management, and configuration baselines mapped to HIPAA and HITRUST.
Continuous monitoring identifies configuration drift as it occurs — the exposure most frequently behind cloud data incidents in our industry.
-
Departmental cloud adoption is common and rarely centrally governed. We bring imaging archives, research environments, telehealth platforms, and clinical SaaS under a single posture without disrupting the workflows that adopted them.
-
Analytics, actuarial, and care management workloads process member data at volume, often across multiple lines of business with different regulatory obligations. We enforce data segregation, residency, and entitlement controls that hold up under CMS and state examination.
-
We document shared responsibility boundaries explicitly. The controls most often missed are the ones each party assumed the other was managing.
Infrastructure Security - Network, Systems & Mobile
Zero Trust principles applied to the environment you actually operate.
Network. Segmentation separating clinical, corporate, guest, and IoT traffic; next-generation firewall and secure access service edge management; encrypted remote access for a distributed workforce.
Systems. Endpoint detection and response, server hardening, and vulnerability management prioritized by exploitability and operational consequence rather than severity score alone, with privileged access governed throughout.
Mobile. Device and application management across personally owned and organization-issued endpoints, with containerized Personal Health Information (PHI) and conditional access that respects how people actually work.
-
The defining challenge is the connected device estate — infusion pumps, imaging systems, monitoring equipment, and biomedical assets that cannot accept an agent or a patch and cannot be taken out of service. We provide discovery, classification, and compensating controls for that population, and design segmentation that isolates clinical technology without interrupting it. Mobile programs are built for shared workstations, badge-tap workflows, and clinicians moving across units and facilities.
-
The defining challenge is scale and distribution — remote and hybrid workforces, contact centers handling PHI by phone, and network connectivity to providers, Third-Party Administrators (TPAs), Pharmacy Benefits Managers (PBMs), and delegated entities. We secure those connections and the identities that traverse them, with particular attention to contractor and offshore access to member data.
Application Security & Governance
Securing what you build, what you purchase, and what you connect.
We embed security throughout the development and procurement lifecycle: secure Software Development Lifecycle (SDLC) practices, static and dynamic application testing, API security and gateway governance, software composition analysis, and penetration testing on a defined cadence.
-
Attention focuses on patient portals, scheduling and intake applications, clinical integrations, and the interface estate that connects the EHR to ancillary and payer systems.
-
Laser-like focus on member and provider portals, eligibility and claims APIs, mobile member applications, and the data exchange layer that connects core administrative platforms to vendors and delegated partners.
-
Governance extends to the vendor ecosystem. Supply chain and internal staff activities now account for a substantial share of healthcare breaches, and an annual questionnaire will not detect it.
Elevance Systems provides structured onboarding assessment, contractual security requirements, and ongoing monitoring of the partners who hold your data.
Risk & Compliance Services
A continuous state of readiness, not a periodic exercise.
We build and manage programs aligned to the HIPAA Security and Privacy Rules, HITRUST CSF, NIST CSF and 800-53, PCI DSS where payment processing applies, and applicable state privacy and breach notification requirements. Services include formal risk assessment and risk register management, control design and testing, policy development and lifecycle governance, third-party risk oversight, and audit support, including HITRUST certification readiness.
-
We align the program to HHS 405(d) healthcare cybersecurity practices and support Joint Commission, state health department, and cyber insurance requirements — coordinating with emergency preparedness so security incidents are handled within the same command structure as any other operational disruption.
-
We align the program to CMS program requirements across Medicare Advantage, Medicaid managed care, and Marketplace lines, alongside state department of insurance expectations and NAIC data security model law where adopted. Delegated entity oversight is treated as a core control, not a procurement formality.
Wherever the underlying systems allow, evidence collection is automated—so documentation becomes a product of daily operations rather than a quarterly scramble.
We report risk in the language leadership already uses: likelihood, financial exposure, and operational impact.
User Awareness Training
The control that technology cannot provide.
Most healthcare breaches still begin with a person acting in good faith under pressure. Training changes that outcome only when it is relevant to the role and reinforced over time.
Foundational. Organization-wide awareness covering phishing, social engineering, credential hygiene, physical security, and incident reporting — delivered continuously and measured through simulated campaigns and behavioral change rather than completion percentages.
-
Clinicians and nursing staff managing PHI under time pressure on shared workstations; registration and revenue cycle teams; biomedical and facilities personnel who introduce connected technology; and physician leadership accountable for clinical governance.
-
Member service and contact center representatives who are the primary target of social engineering; claims and enrollment operations handling financial and eligibility data; care management teams working with clinical records; and sales, broker, and vendor-facing staff operating outside the corporate perimeter.
-
Technical staff with privileged access, and executives and board members who are simultaneously high-value targets and accountable for governance.
A Case for a Managed Program
A security program of this scope requires specialized talent across six disciplines, sustained across three shifts, retained in a market where healthcare organizations compete directly with technology companies for the same professionals.
Partnering with Elevance Solutions provides mature capability from the outset, continuous coverage without single-person dependency, compliance evidence generated through routine operations, and predictable operating costs instead of an open-ended internal investment. Defined service levels govern performance, and we report it in terms your leadership and board can act on.
Begin with a Security
& Risk Posture Assessment.
Within 30 days, your leadership team receives a current-state evaluation across all six domains, a remediation roadmap prioritized by risk reduction relative to investment, a compliance gap analysis mapped to the frameworks that govern your organization, and a board-ready summary of your risk position.
-
Includes connected medical device exposure and clinical downtime readiness.
-
Includes delegated entity and vendor risk across every line of business.